Custom AI insights
AI Agent Permissions for Small Business: Give Systems Only the Access They Need
Useful AI agents need access to business tools, but not unlimited access. Least privilege, approval gates, and clear logs make connected workflows safer and easier to operate.
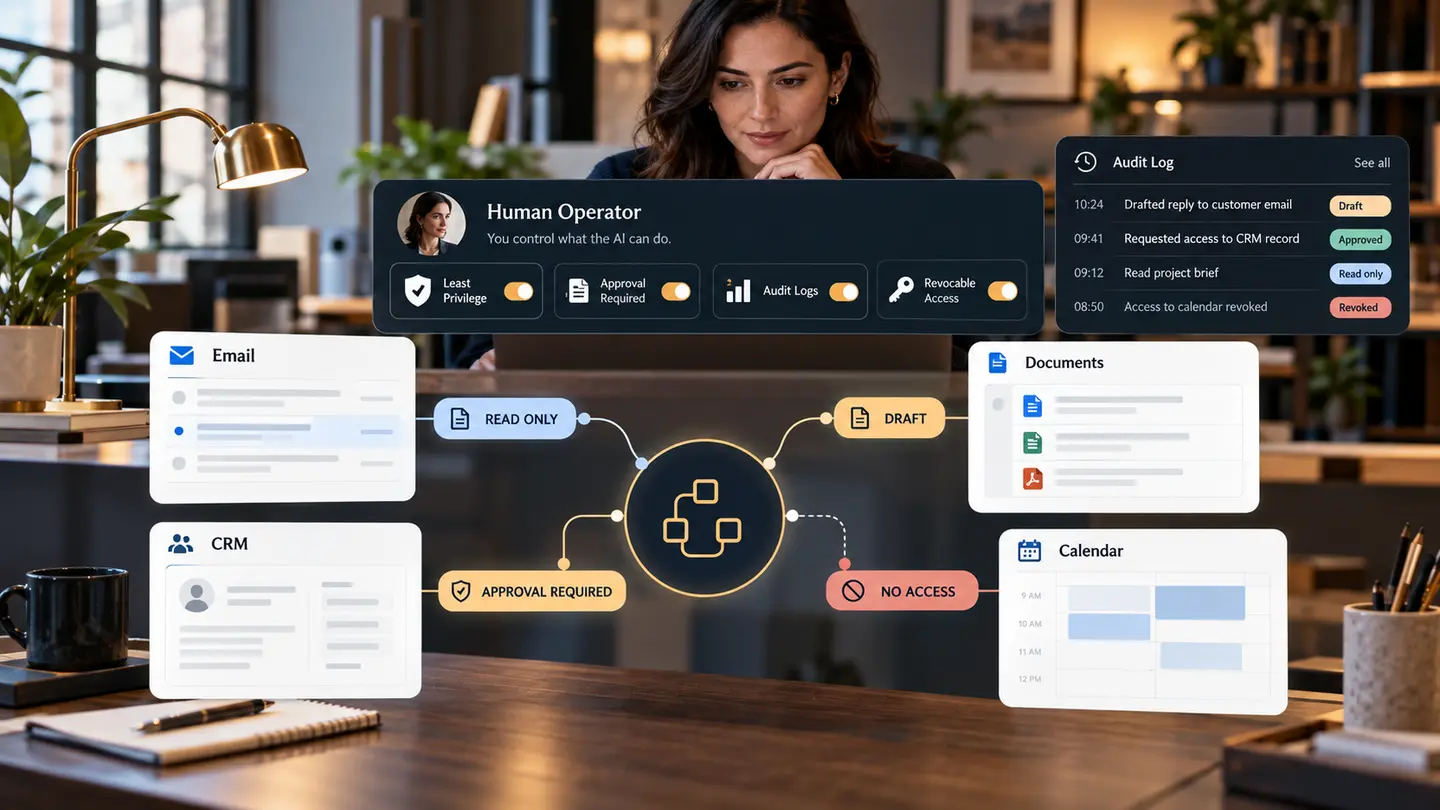
An AI agent becomes more useful when it can work with business tools. It can read a shared inbox, look up a customer record, search documents, prepare a task, or update a field.
That usefulness creates a basic design question: what should the system be allowed to access and change?
The safest answer is rarely “everything.” A well-designed agent receives the smallest set of permissions needed for a defined job, uses approval gates for consequential actions, and leaves a record that people can review.
This approach is called least privilege. It is not only a security rule. It also makes the workflow easier to understand, test, and trust.
Start With the Job, Then List the Required Access
Define the agent’s responsibility in operational terms. “Help with customer service” is too broad. “Read new support messages, retrieve approved policy information, prepare a reply, and route refund requests to a manager” is specific enough to map.
For each step, list what the agent must read, what it may create, what it may update, and what it must never do. If a permission does not support the defined job, leave it out. Access should follow the workflow instead of being granted because a connection is available.
Separate Read, Draft, and Act Permissions
Reading information is different from changing it. Preparing an action is different from completing it.
An inbox assistant may need permission to read selected messages and save a draft without permission to send. A CRM assistant may create a proposed update in a review queue instead of changing the customer record directly. A scheduling assistant may show available times without canceling an existing appointment.
Separating these levels creates a useful path for gradual rollout. The agent can begin in read-only or draft mode, prove that it handles the workflow reliably, and earn narrow action permissions only where the business sees a clear benefit.
Use Separate Service Accounts When Possible
Do not run a shared business workflow through the owner’s personal account simply because that account can access everything.
A dedicated service account or tightly scoped integration makes permissions easier to see and revoke. It also avoids accidental access to unrelated email, files, contacts, or administrative settings. The exact setup depends on the software, but the principle is consistent: the automation should have its own identity and only the roles it needs.
Limit the Records, Folders, and Mailboxes in Scope
A permission can look narrow while still exposing too much information. “Read Drive” may include HR files, financial documents, customer exports, and old folders the workflow never needs.
Scope access to specific folders, labels, queues, databases, fields, or record types when the connected system supports it. If technical limits make that impossible, consider a controlled staging area that receives only the documents or records approved for the agent. Good data boundaries are often more important than clever prompts.
The same boundary can protect sensitive licensing and insurance records.
Scope each workflow to limit which history the agent may retrieve for the person and task in front of it.
Require Approval for Consequential Actions
Money, legal commitments, account changes, sensitive messages, deletions, and broad external communication deserve additional control.
The agent can gather context, prepare the change, and explain why it recommends the next step. A person with the right authority should approve the action. For lower-risk work, rules may allow automatic completion within clear limits. The key is placing approval where the consequence rises rather than treating every action the same.
Protect Secrets and Credentials
API keys, passwords, access tokens, and connection credentials should be stored in secure configuration or credential-management tools, not pasted into prompts, documents, or chat history.
Employees should not need to reveal a password to make an agent work. Access tokens should be revocable, permissions should be reviewed, and credentials should be rotated when appropriate. If a provider cannot explain how credentials are stored and used, the connection is not ready for business data.
Keep an Audit Trail That Answers Practical Questions
Logs should make it possible to determine what the agent read, which action it proposed or completed, when it happened, which rule or user request triggered it, and whether a person approved it.
Not every workflow needs a forensic security platform. It does need enough history to investigate a mistake, correct a bad record, and understand whether the problem came from the source data, the AI interpretation, a workflow rule, or a human approval.
Plan for Errors, Revocation, and Offboarding
Access should be easy to reduce or remove. Know who can disable the workflow, revoke a connection, stop outbound actions, and recover from an incorrect update.
Review permissions when the agent’s job changes, an integration is replaced, an employee leaves, or the business adds a new data source. Old access tends to accumulate quietly. A periodic permission review is a practical maintenance task, not unnecessary paperwork.
Test Permissions, Not Just Answers
A system can produce excellent answers and still be unsafe if it can reach unrelated data or perform unintended actions.
Testing should include attempts to access out-of-scope records, follow instructions hidden in untrusted content, send without approval, change protected fields, or continue after access is revoked. Verify that failures are visible and that a person can stop the workflow. Permission boundaries are part of product quality.
Start in Read-Only or Draft Mode
Choose one workflow and begin with the least powerful version that can still create value. Let the agent retrieve approved information, prepare a draft, and show its proposed action. Review the results and exceptions.
If direct action would save meaningful time, add one narrow permission with limits and logging. This staged approach is slower than granting broad access on day one, but it is usually faster than cleaning up a system that changed the wrong records at scale.
Want an AI Workflow With Clear Boundaries?
If you are considering an AI agent that connects to your inbox, documents, CRM, or other business software, we can help map the job, required access, approval points, and recovery path before the system receives authority.
Design the Access Before You Connect the Agent
We can help map the workflow, limit permissions, place approvals, and build a recovery path before an AI system touches important business tools.
Discuss a Custom Build ↗